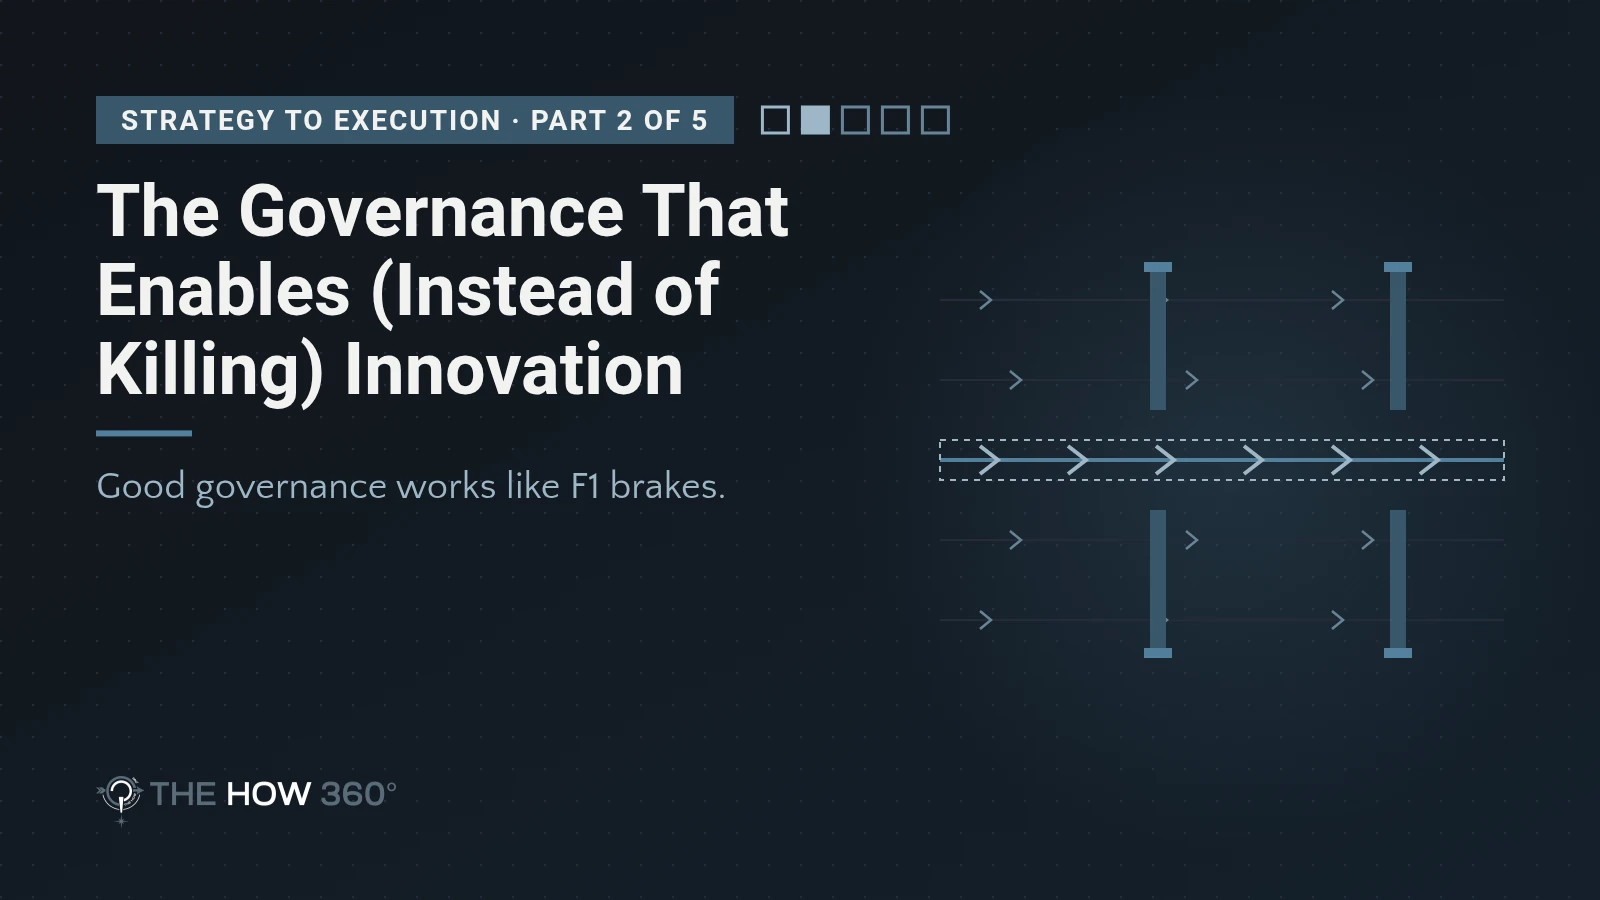
Governance is often seen as a roadblock. But true governance should be like F1 brakes: the reason you can drive 300 km/h safely. Here is how to build it.
Strategy to Execution, part 2
In Formula 1, the brakes are not there to slow the car down. They are there so the driver dares to go 300 km/h. Governance should work the same way.
Most governance does the opposite. It adds checkpoints, slows teams down and pushes them towards workarounds. In this article I show why heavy governance creates more risk, not less, and give you a "Yes, if" framework and a short control audit you can use to make governance an enabler again.
Watch an F1 pit stop. You do not see chaos. You see highly synchronised procedures playing out in seconds. Strict rules do not have to slow you down. Done well, they are the reason you can move fast.
That is the standard I hold governance to. Does it let us go faster with confidence, or does it just make us slower?
We often hear the call for "agility," followed immediately by a stack of new mandatory checkpoints being added to the project lifecycle. That is where innovation dies. When governance is seen only as a control mechanism, it becomes the friction point that disconnects strategy from execution.
Three patterns show up again and again:
Here is the irony. The more control we layer on in the name of safety, the more risk we create.
When governance gets too heavy, high-performing teams do not just slow down. In my experience, they find workarounds: shadow IT and shadow processes that keep them productive. The result is that you lose visibility, and suddenly you have no governance at all.
Real safety comes from trust that is verified by automated, lightweight systems, not from administrative friction.
To break the paradox, replace manual checkpoints with transparency. Picture an executive compliance dashboard that gives the board the comfort it needs without a 100-page report. It shows that governance is working in the background, so the business can keep its speed while managing its risk in real time.
The fix is what I call progressive compliance: governance built into the daily workflow instead of being a separate event.
The "Yes, if" framework has three steps:

The best public example I know comes from a heavily regulated place: the US Food and Drug Administration.
The team behind the FDA's Emergency Operations Network Incident Management System worked inside a lifecycle framework with ten phases, each ending in a stage-gate review. Getting documents approved could take up to four weeks, which does not fit a sprint rhythm (Agile Alliance).
They did not ignore the rules. They tailored them, with formal approval. They combined the design, development and test gates into one review cycle and used sprint planning and sprint reviews to get the go/no-go from the stakeholders. Documentation was estimated per story, given an owner, written during the sprint, and supported by a technical writer and pair writing.
The result, as the team reports it: less time spent on stage-gate reviews, shorter gaps between documentation deliveries, better defect removal, and a programme that grew to more stakeholder groups and more funding. Same compliance. Less friction.
That is "Yes, if" in practice.

Better governance does not start with the perfect framework. It starts with what you do on Monday morning.
In my experience, the audit takes about two weeks, and the first three automated checks about four more.
Common mistakes to avoid:
Good governance works like F1 brakes. It is the reason you can go fast, not the reason you go slow.
Heavy, manual governance creates the very risk it is meant to prevent, because people route around it. Light, automated and visible governance keeps everyone inside the system.
The best governance is the kind you barely notice, because it is part of how the work gets done.
So how many of your controls would survive the question "when did this last catch something?"
Read next: Part 3 of the series, The Translation Layer: Bridging Sales & Delivery. If you missed part 1, start with Why 90% of IT Strategies Fail, and How to Fix It.
Want governance that speeds you up? See how I help leadership teams with IT Leadership Consulting & Strategy Execution.
Stay up to date with our informative blog posts.
Struggling with complex projects, IT leadership challenges, or strategic execution? With over 30 years of experience in delivering high-impact results—whether rescuing delayed initiatives, optimizing resources, or driving transformation—I provide the clarity, structure, and leadership needed for success.
Let’s discuss how I can help you achieve your goals. Schedule a call today!

We only use necessary cookies unless you agree to statistics (Google Analytics), which help us see which articles are read. You can change your choice at any time. Read the privacy policy